At ASP OL Media, compliance is not a checkbox at the end of a campaign brief. It is built into every list we manage, every campaign we send and every technical configuration we deploy. We help businesses send emails that reach inboxes, protect recipients and meet all regulatory standards applicable to their audiences in India and internationally.
We do not send to purchased or unverified lists. Every contact we send emails to has a verifiable trail of consent.
Ensure that SPF, DKIM and DMARC are properly configured for all sending domains before sending your first campaign.
Remove hard bounces after every send and manage inactive contacts on a regular schedule, ensuring a clean list and an intact reputation.
We manage campaigns that comply with applicable standards such as TRAI, the IT Act, GDPR, CAN-SPAM and CASL.
We keep track of complaint rates with all major inbox providers and take action before problems get out of hand.
Unsubscribe requests are automatically honoured immediately. There are no delays, no exceptions.
Many businesses see email compliance as just a legal box to check, separate from their marketing goals. But that’s not the case. The same steps that protect your programme from legal issues also help it perform better.
When you use permission-based lists, your open rates go up because people want your emails. Sending from authenticated domains helps your messages reach the inbox, not the spam folder. Keeping your lists clean boosts engagement on every campaign. Using honest subject lines builds trust, which turns subscribers into customers.
Email programmes that don’t follow the rules don’t just risk legal trouble. They also tend to perform poorly. If you cut corners on compliance, you could end up with blacklisted IPs, a damaged sender reputation, more complaints and your emails landing in spam. We’ve seen companies come to us after these problems have already hurt their results.
Building your email programme on a compliant foundation isn’t just the safe choice. It’s also the smart move for your business.
Email marketing is subject to multiple sets of regulations simultaneously. The regulations that apply to your programme depend on where your subscribers live, not just where your business is located. Here is what every sender needs to know.
TRAI’s Unsolicited Commercial Communications framework requires businesses sending commercial communications to Indian recipients to follow applicable requirements relating to sender registration, consent, customer preferences and consent records. Non-compliance can result in complaints, penalties and restrictions on commercial communications.
The IT Act governs data collection, storage and usage for electronic communications in India. Key obligations include obtaining informed consent before collecting subscriber data, maintaining reasonable security practices and giving subscribers meaningful control over their personal information.
India’s Digital Personal Data Protection Act (DPDPA) will significantly raise the bar when it comes into full force, introducing stricter consent requirements, mandatory breach notification timelines and stronger individual data rights. Businesses that build compliant programmes now will transition smoothly. Those who do not will be scrambling to catch up.
We stay ahead of these developments and update our practices accordingly, so our clients are never caught off guard by a regulatory change.
GDPR applies to any business that sends emails to people in the EU, regardless of where the business is located. If you have EU subscribers on your list, you must comply with GDPR.
The core requirements: free, specific and unambiguous consent before sending any marketing email; documented consent that can be produced on request; a clear and immediate unsubscribe mechanism in each email; and complete respect for data subject rights, including the right of access, rectification and erasure.
Failure to comply with GDPR can result in penalties up to €20 million or 4% of global annual turnover. The practices GDPR requires are good email marketing practices, no matter where you are in the world, which is why we treat GDPR as a global standard, not a European problem.
Many business senders are surprised to learn that CAN-SPAM covers commercial email to US recipients and includes both B2B email and consumer campaigns. Requirements include honest, non-deceptive subject lines; a valid physical postal address in every email; a clear unsubscribe mechanism and unsubscribe requests honoured within 10 business days.
CAN-SPAM isn’t as strict as GDPR, but it does have real penalties for non-compliance, and its honesty requirements for subject lines are ones we hold ourselves to on every campaign we run, no matter where the recipient is.
CASL is one of the most stringent email marketing laws in the world. This means that you need express or implied consent before sending any commercial electronic message to a Canadian recipient. You need to clearly identify yourself as the sender in each message. You need to have an unsubscribe mechanism that works and is honoured within 10 business days.
Critically, CASL shifts the onus of proof from the recipient to the sender to establish the existence of valid consent. CASL requires businesses to be able to demonstrate that they obtained valid consent. Consent records are your legal defence.
Most email compliance issues don’t come with a legal warning or a regulatory penalty. They show up gradually in your campaign metrics, and by the time you see the damage, it’s often been building for weeks or months. Watch out for these warning signs:
Your open rates are on a steady decline: You haven’t changed your content or sending frequency. Declining open rates are often the first indication that inbox providers are filtering your campaigns into spam folders instead of the primary inbox.
Your bounce rate is above 2%: Hard bounces above 2% can indicate that your list hasn’t been well-maintained. High bounce rates can signal poor list hygiene to inbox providers, which can hurt your sender reputation.
You’re getting unexpected spam complaints: If your subscribers are marking your emails as spam instead of just unsubscribing, it usually means they don’t remember signing up, you’re sending too many emails or your content doesn’t match what they signed up for. Any of these is a problem of consent and relevance.
Your emails are always in the Promotions tab in Gmail: This isn’t a spam folder, but the Promotions tab doesn’t necessarily indicate a problem with your sender reputation. Engagement issues and authentication gaps can contribute to delivery problems.
You have never set up SPF, DKIM or DMARC: If you don’t have all three authentication records correctly set up for your sending domain, you’re sending without the baseline trust signals that modern inbox providers require. Your campaigns could be filtered or rejected, even if your content is excellent.
Unsubscribe rate jumps with every send: A consistently high unsubscribe rate indicates a gap between what subscribers expect and what you are actually sending—a relevance and segmentation issue with compliance implications as audience frustration grows.
You don’t know where your list came from: If you have a database built over years from multiple sources and can’t trace the consent origin of a significant portion of your contacts, you have a compliance risk that needs to be addressed before your next campaign.
If any of these apply to your current email programme, the right move is an audit, not another campaign.
At ASP OL Media, compliance is not a policy document gathering dust on a shelf. It is an active, ongoing practice and part of how we run every client programme.
We look at how a client’s list was built before we ever send an email on their behalf. Any segment that can’t show verifiable consent is flagged and suppressed until it can be properly re-permissioned. We want to mail a smaller opt-in list, not a larger non-opt-in list.
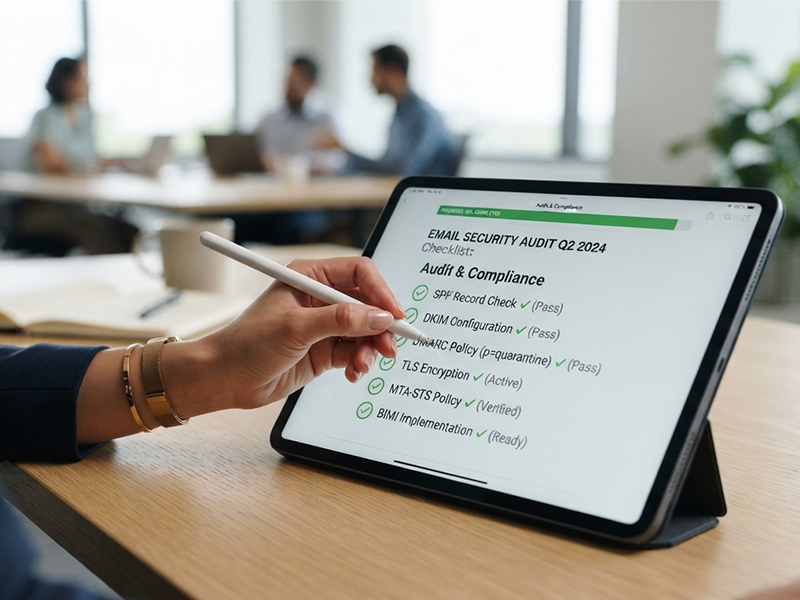
Before any campaign launches, we validate and properly set SPF, DKIM and DMARC records. We don’t guess. We verify. For new sending domains, we manage IP warming schedules that gradually and safely build sender reputation before high-volume sends start.
Hard bounces are taken out right after each campaign. Soft bounces are tracked and handled above set thresholds. Inactive subscribers are identified on a rolling basis and either moved into a re-engagement flow or suppressed before they begin to negatively impact engagement metrics and future deliverability.
When a subscriber clicks ‘Unsubscribe’, they are instantly removed from the active list. No re-subscription loop. No dark pattern that makes it harder than it should be to opt out. We build suppression lists and apply them to all sends, without exception.
We monitor complaint rates on Google Postmaster Tools, Microsoft SNDS and other inbox provider reporting tools. If complaint rates approach an unacceptable threshold, usually around 0.08% for Gmail, we pause the campaign segment, diagnose the cause and implement corrective measures before the issue escalates.
Email marketing regulations are not static. TRAI updates its framework, GDPR guidance changes and India’s DPDPA implementation is ongoing. We monitor these changes and proactively update our compliance practices so that our clients are prepared for regulatory changes, rather than waiting to respond after they have already created risk.
We don’t just take over sending when a new client comes to us with an existing email programme. We also conduct a thorough compliance and deliverability audit before any campaign goes out under our management. This is what that includes:
We begin with the list itself. Where did the contacts come from? How was consent obtained? Are there segments where the source of consent is unclear or unprovable? We sort the list by the quality of consent and mark any segments that need to be re-permissioned before they can be safely mailed.
We look at the bounce rates, open rates, click rates and complaint rates of past campaigns. This analysis tells us the present health of the list, how inbox providers are treating the sending domain and where the most urgent hygiene work needs to happen.
We check each client’s sending domains and subdomains for SPF, DKIM and DMARC records. Any misconfigured or missing authentication records are corrected before any campaign is launched. We also check BIMI records for clients who want their brand logo in the inbox—a trust signal that’s becoming increasingly important for high-volume senders.
We verify the client’s sending IPs and domains against major blacklists, including Spamhaus and Barracuda, using tools such as MXToolbox. If an IP or domain is blacklisted, it must be remediated before sending can resume. The remediation process varies based on the blacklist and the reason for the listing.
We ensure that the unsubscribe functionality works correctly for all active campaigns and that suppression lists are complete and applied consistently. Gaps in suppression list management are one of the most common compliance risks we see in inherited email programmes.
We audit the client’s email content, consent documentation and sending practices against the regulatory frameworks that apply to their audience: TRAI, the IT Act, GDPR, CAN-SPAM or CASL, depending on where their subscribers are located. We document and address any gaps before we take over campaign management.
We use Google Postmaster Tools, Microsoft SNDS and other inbox provider reporting systems to assess the client’s current sender reputation, spam rate trends and domain reputation status. This provides a baseline against which we can measure improvement as compliant sending practices are implemented.
At the end of the audit, we provide a clear written report on what we found, the risk level of each issue and the remediation steps we recommend, including the prioritised action plan and timeline. No buzzwords, no vague recommendations, just a clear picture of the programme’s status and exactly what needs to happen next.
The audit usually takes between five and seven working days, depending on the size and complexity of the existing programme. For most clients, it uncovers issues they didn’t know they had and provides a clear platform to build a programme that performs consistently from day one.
Whether you run your email programme in-house or with an agency, these are the non-negotiable practices that underlie every compliant, high-performing email programme.
Only send to people who have asked to hear from you: Everything is based on permission. A list based on real opt-ins will generally outperform a larger list based on assumptions, purchases or scraping.
Wherever feasible, use double opt-in: By sending a confirmation email that confirms a new subscriber’s address and intent, you end up with a cleaner list, stronger consent documentation and better long-term engagement.
Use subject lines that really say what’s in your email: Most rules outlaw misleading subject lines, which erode sender-subscriber trust over time—the engine of long-term email performance.
Your email must have a physical address: It is a legal requirement under CAN-SPAM and a trust signal under other frameworks. It takes little time to add and costs nothing.
Make it easier to unsubscribe than to remain subscribed: If a subscriber can’t easily get out, they’ll complain instead. And a spam complaint will do far more damage to your sender reputation than an unsubscribe ever will.
Regularly clear out your list: A small, engaged list beats a big, neglected list on every metric that matters, including open rate, click rate, deliverability and return on investment.
Verify your sending domain: SPF, DKIM and DMARC are not optional technical housekeeping measures. These are the baseline trust signals that inbox providers use to decide if your email is legitimate. And without them, even the best campaigns don’t perform well.
Use your metrics as compliance signals: Increasing complaint rates, decreasing open rates and increasing bounce rates are not just performance issues but also early warning signs of compliance issues that will compound if not addressed.